


< !--cell-- >
< !--end grid-x-->


Cybersecuring Payments
Are we losing the fight against next-gen bank robbers?
Econ Focus
First Quarter 2014
Cover Story
It isn’t the kind of holiday news retailers want to deliver. On Dec. 19, 2013, Target announced that its payment terminals and computer systems had been hacked, allowing criminals to access credit and debit card data for as many as 40 million shoppers during the busy Black Friday weekend. The hackers also stole personal information for 70 million customers. In January, department store Neiman Marcus said that payment card information for its customers had been compromised, and arts and crafts chain Michaels said it was looking into a possible breach.
Breaches of payment systems at large retailers are not new. In 2007, hackers stole 45 million customer records from TJX Companies, the parent of T.J. Maxx. To date, such events have not changed the habits of most consumers: In the United States, plastic is king. Cards accounted for two-thirds of noncash payments in 2012, increasingly displacing cash, checks, and other forms of payment, according to a 2013 Fed study of the payments system. But with convenience comes risk. The Fed’s study found that payment cards were used in 92 percent of fraudulent transactions, with checks and electronic check transfers making up the remainder.
Cyberattacks have been growing in magnitude. While the number of reported data breaches (including both attacks on payment systems and other attacks) trended down to 2,164 in 2013 from 3,140 the previous year, hackers made off with over three times as many records: 823 million compared with 264 million.
According to a 2013 survey by Verizon, the most commonly targeted sectors were financial institutions and retailers, and payment card information was by far the most stolen type of data. That may not be surprising, given that one of the primary motivations for breaches identified by the Verizon report is financial gain. But an equal percentage of attacks were classified as "opportunistic," which raises the question: Is the payments system an easy target?
During a series of congressional hearings following the Target breach, legislators pointed to the prevalence of chip-and-PIN technology in other developed economies (known as "EMV" for developers Europay, MasterCard, and Visa). These so-called "smart" cards use an embedded microchip to process payments, allowing for more secure authentication that makes intercepted data from any one transaction largely useless to fraudsters. American cards still rely on magnetic stripes, the same technology that powers cassette tapes, to relay static payment data that can be intercepted and copied onto blank cards for fraudulent use. Many have argued that the old cards are well past their prime.
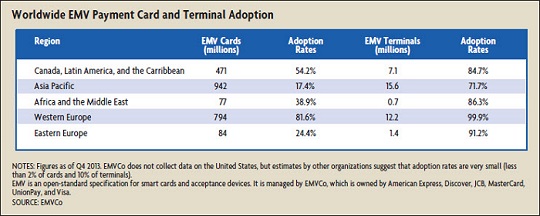
The major card brands — Visa, MasterCard, and Discover — announced their intent to hold merchants who have not upgraded to EMV by October 2015 responsible for fraud that could have been prevented by a smart card. Target plans to be an early adopter, beating the deadline by several months. But EMV is not entirely new — the technology debuted two decades ago. In fact, Target introduced smart cards at its stores in the early 2000s but abandoned the effort after a year, citing costs and consumer complaints that the new cards complicated checkout. The United States was a pioneer of payment cards but has been much slower to adopt smart cards. According to Javelin Strategy and Research, only 10 percent of payment terminals and less than 2 percent of cards in the United States are EMV compatible, compared with much higher numbers worldwide (see table). Has America fallen behind the times, and if so, why?
 Download article
Subscribe to Econ Focus
Receive an email notification when Econ Focus is posted online.
By submitting this form you agree to the Bank's Terms & Conditions and Privacy Notice.
Contact Us